Governance, Compliance & Audit Intelligence
Explore how control information, system configurations and audit evidence could support human-reviewed governance and compliance analysis.
A roadmap scenario based on the original CIRMS GL5 use case. Not a production deployment or a guaranteed outcome.
Turn scattered evidence into a reviewable picture.
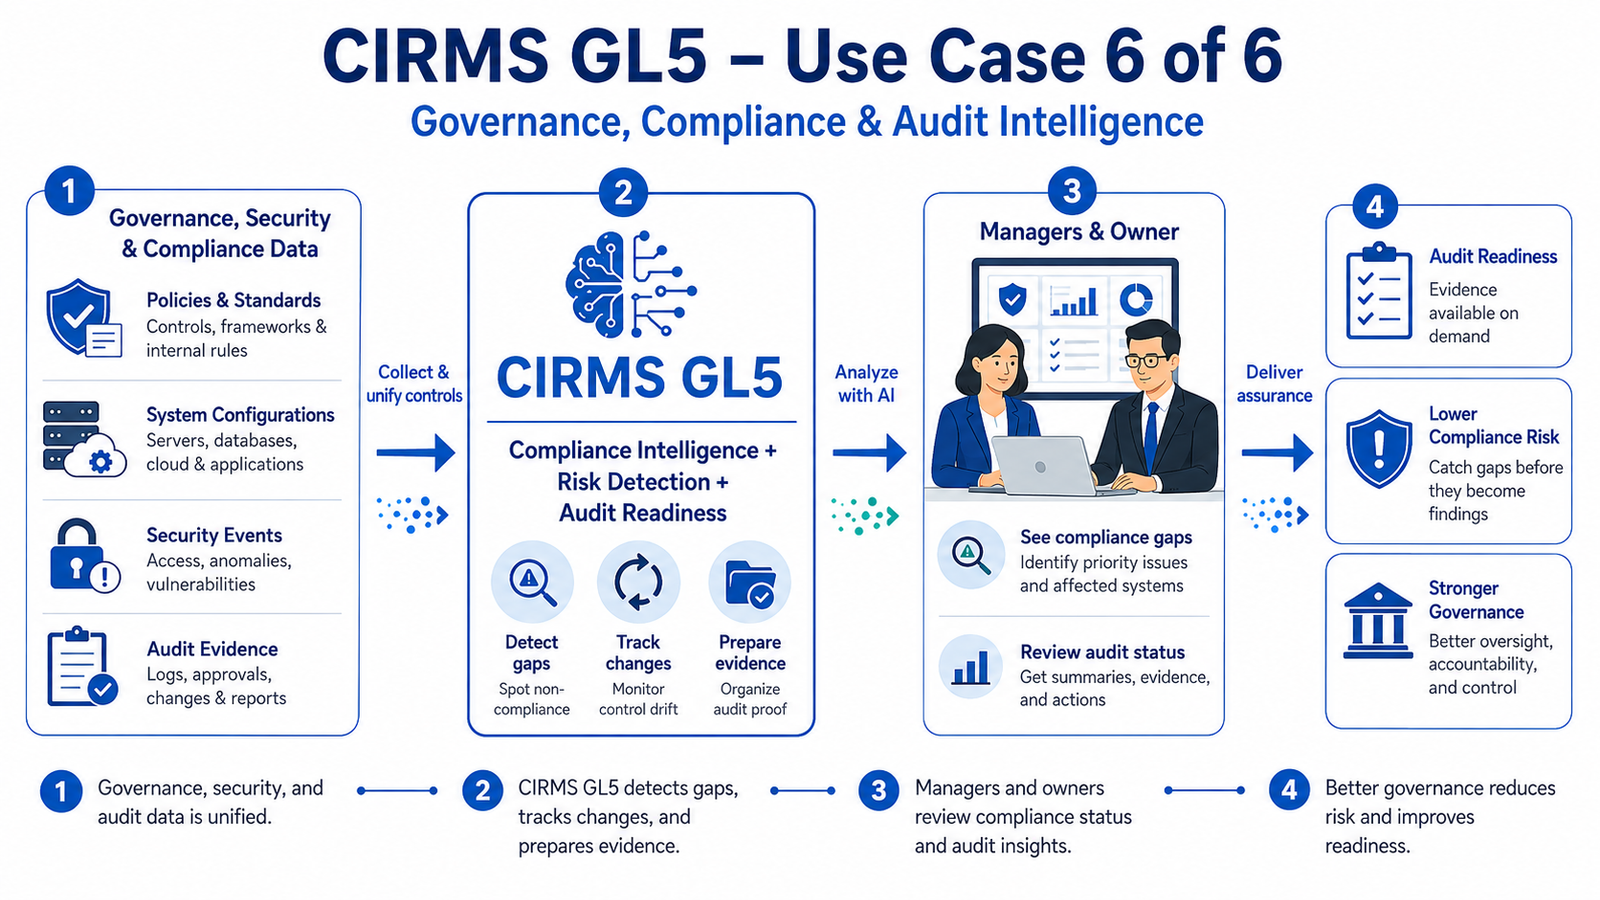
Policies, configurations, security events and audit evidence are not always reviewed together. The CIRMS concept proposes connecting them to help people detect potential gaps, track changes and prepare evidence for review.
Information in scope
- Policies & standards
- Internal rules, control definitions and selected frameworks.
- System configurations
- Approved infrastructure, application and database records.
- Security events
- Available access records, anomalies and event information.
- Audit evidence
- Logs, approvals, changes and supporting reports.
How the scenario could work.
Follow the proposed path from approved information to AI-assisted review and a decision owned by people.
- 01
Unify the evidence
Define controls and map the approved evidence sources to the review scope.
- 02
Explore planned GL5 analysis
Assist with potential-gap detection, change review and evidence organization.
- 03
Review findings
Responsible people verify context, exceptions and possible false positives.
- 04
Prepare an accountable response
Record the review outcome and coordinate actions with control owners.
Audit preparation
Make relevant evidence easier to locate and review.
Earlier gap review
Surface potential issues for qualified human assessment.
Stronger oversight
Clarify the relationship between a control, its evidence and its owner.
The original use-case concept.
What sits behind the use case.
Separate the platform foundation from planned intelligence and the requirements of the target environment.
GL3 / GL4 & architecture
GL3 operational records and GL4 prepared knowledge can form an information foundation for an agreed governance review. Evidence retention and integrity controls need to be specified for the deployment.
AI & future extensions
AI-assisted control-gap detection, evidence summaries and compliance intelligence are GL5 roadmap concepts. They do not establish that an organization is compliant.
People, data & permissions
Map the applicable controls, responsibilities, access restrictions and review process. CIRMS is not presented as a certification, a legal determination or a replacement for an auditor.
A bounded evaluation
Select one control family and a limited evidence set. Have the control owners compare the proposed summaries with their existing review process.
Candidate measures: evidence completeness, retrieval time, reviewer agreement and the number of suggestions rejected or corrected during validation.